CVE-2026-92392 in curl: Why HTTP/2 Uploads Need a Dependency-Level Patch Response
curl 8.23.0 fixes a high-severity use-after-free in HTTP/2 uploads. The practical risk depends on how your systems use curl and libcurl, so inventory, update paths, and upload workflows matter more than a dramatic headline.
A high-severity flaw in curl and libcurl changes the usual way people think about client-side security. CVE-2026-92392 is triggered during an HTTP/2 upload, but the hostile party is the server receiving the upload. A malicious server can send a particular stream-reset response while a client is transmitting data, leaving curl with a reference to an object that has already been freed. The result is memory corruption, and the curl project says the bug has been shown to be convertible into remote code execution when a demanding set of build, architecture, allocator, timing, and protocol conditions line up.
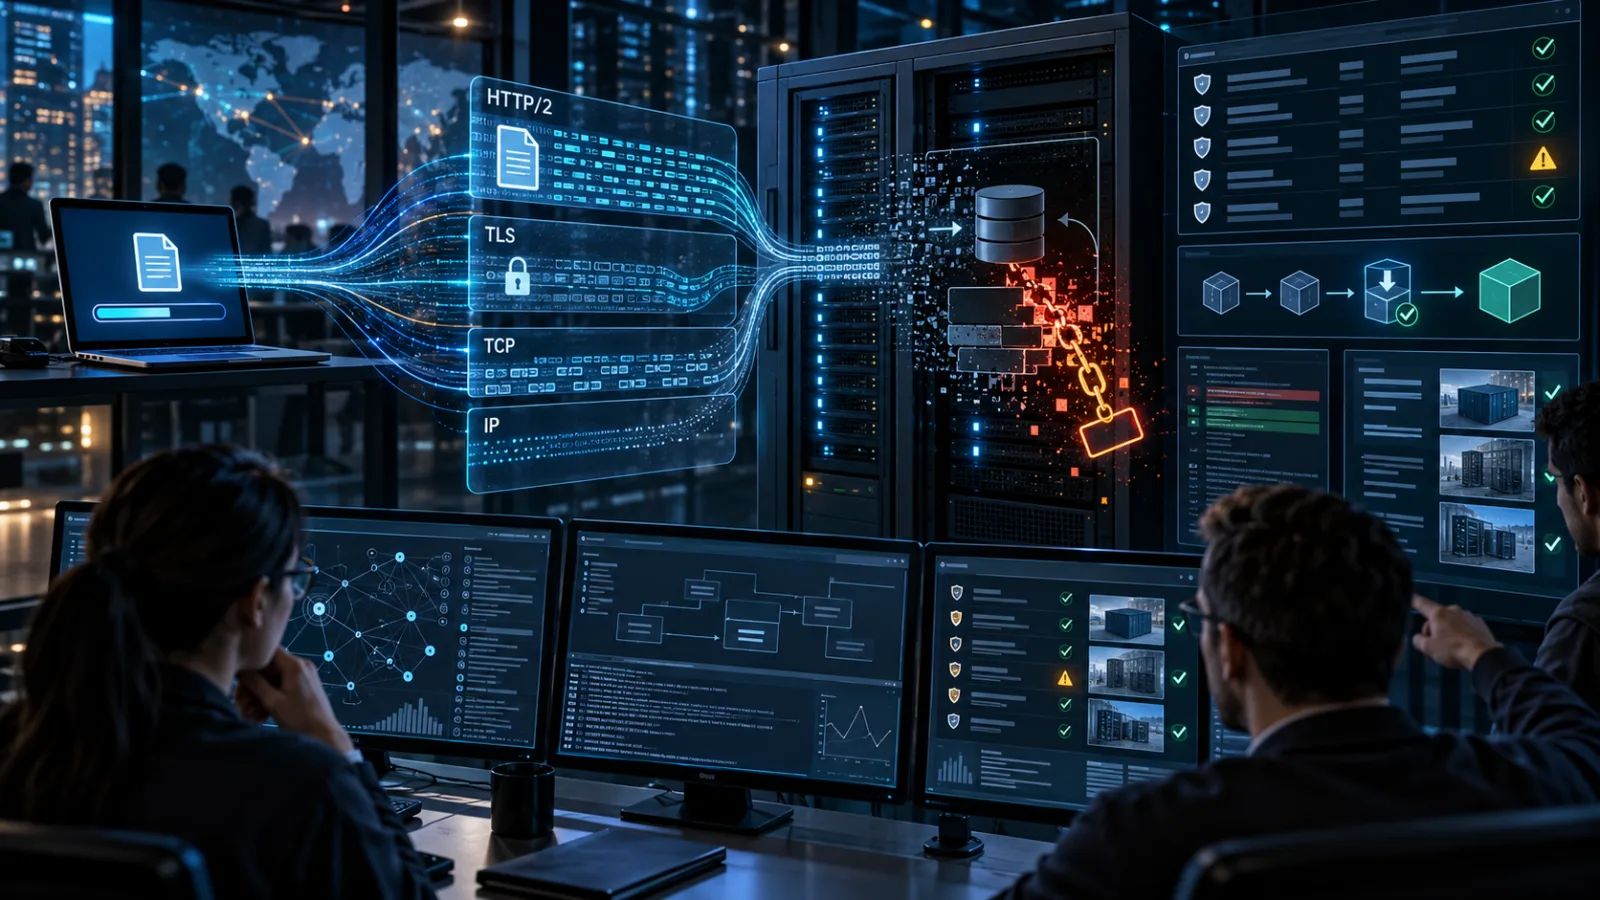
The fix is in curl and libcurl 8.23.0, released on October 14, 2026. The affected range is 8.12.0 through 8.22.0. That range matters because libcurl is frequently embedded in applications, operating-system components, automation tools, package managers, security products, and services that do not advertise their use of curl. Updating the command-line binary on one administrator’s workstation may therefore leave the more important copies untouched.
This is a patching story, but not a simple “run the update everywhere” story. The first job is to discover where curl is used for uploads over HTTP/2, including through a library or statically linked application. The second is to decide whether a temporary reduction in protocol capability is practical while the permanent fix moves through vendor packages and production change windows. The third is to check whether the systems that upload files can be trusted to contact only intended destinations.
What CVE-2026-92392 actually affects
The curl advisory describes a use-after-free in the HTTP/2 upload path. During an upload, the server can issue an HTTP/2 RST_STREAM with the reason HTTP_1_1_REQUIRED or REFUSED_STREAM. The connection itself can remain alive while the individual transfer is stopped. In the vulnerable state machine, curl later cleans up the transfer and the connection in an order that leaves a dangling reference to the transfer object.
A use-after-free does not automatically mean that every invocation becomes code execution. It means that software continues to use memory after its owner has released it. Depending on what occupies that memory next, the immediate outcome can be a crash, corrupted state, information exposure, or a more controlled memory-safety failure. In this case, the curl project classifies the issue as High severity and documents a path from the memory error to remote code execution.
The affected versions are curl and libcurl 8.12.0 through 8.22.0, inclusive. Versions before 8.12.0 are not affected by this particular flaw, and 8.23.0 contains the fix. The distinction between curl and libcurl is operationally important: the command-line tool is one consumer, while a much larger number of applications may call the library directly. A server that never runs the curl executable can still be exposed through an application linked against libcurl.
The vulnerability requires HTTP/2. That does not mean every HTTPS transfer is automatically vulnerable, but it does mean that teams should not infer safety merely because users did not explicitly pass an HTTP/2 option. curl can negotiate HTTP/2 when connecting to an HTTPS service that offers it and when the local build includes the relevant support. Applications may also select HTTP/2 explicitly through libcurl options or higher-level networking frameworks.
The vulnerable operation is an upload from the client to the server. Ordinary downloads are not the scenario described by the advisory. That narrows the exposure, but it does not make the problem exotic. Backup agents, artifact publishers, telemetry clients, document-ingestion services, CI systems, cloud connectors, customer-support tools, synchronization software, and internal APIs all commonly send data outward. Some use curl for only one small part of a larger workflow, which is exactly why a package inventory alone can miss the practical exposure.
The attacker is on the receiving side
Many defensive playbooks begin with the assumption that the dangerous server is the one serving a download. CVE-2026-92392 reverses that mental model. The client initiates an upload to a server it believes it can trust, and the server can be the component that supplies the hostile protocol behavior.
That does not mean an attacker can exploit any curl process simply by placing a malicious page on the internet. The victim process must connect to a server controlled or influenced by the attacker, perform an upload, negotiate HTTP/2, and satisfy the implementation conditions needed to reach the vulnerable cleanup sequence. In a real environment, this could happen through a deliberately malicious endpoint, a compromised service, a redirected workflow, a user-selected upload destination, or an application that accepts remote configuration. The exact route depends on the surrounding product.
The curl project lists unusually specific requirements for turning the flaw into code execution. The attacker needs knowledge of the exact curl version and object layout, details of the target architecture, a compatible libc allocator and heap layout, predictable effects from nghttp2 and TLS 1.3, and carefully controlled timing across parallel transfers. The published exploit also has a short-command constraint. Those requirements make reliable exploitation difficult, but they are not a reason to treat the issue as harmless. Modern attack chains often begin with a crash or partial memory corruption and improve as target details become available.
The public record currently distinguishes between exploitability and known exploitation. The advisory documents a proof of concept and a route to code execution under precise conditions. The NVD entry does not provide its own CVSS assessment and does not say that the vulnerability is being exploited in the wild. A public proof of concept is still a meaningful signal for defenders, especially where curl is embedded in long-lived services or updated slowly. It is not evidence that every vulnerable installation has been compromised.
Why the 8.23.0 release deserves careful handling
The fix arrived in a coordinated curl release that also addressed 23 other published security problems, most of them rated Low by the project. CVE-2026-92392 is the release’s single High-severity issue. That grouping creates two competing operational risks. Some teams may see the large number of advisories and freeze because the upgrade looks complicated. Others may update a visible command-line package and assume the entire dependency graph is covered.
The right response is to separate urgency from uniformity. The urgent item is to identify vulnerable builds that perform uploads and move those systems to a fixed vendor package or to curl and libcurl 8.23.0. The implementation path may differ by operating system, container base image, language runtime, appliance, or commercial application. A distribution-maintained libcurl package may backport the fix without changing the reported upstream version in the way a simplistic version check expects. Security teams should therefore confirm the vendor’s advisory and package changelog, not rely on a single string comparison.
The release also changed more than security code. The project removed SMB and SMBS support and introduced other behavior changes and bug fixes. That does not make the upgrade unsafe, but it reinforces the need to test applications that depend on less common protocols, unusual authentication flows, custom TLS backends, or strict file-handling behavior. The security fix should not be delayed for a perfect universal test suite, yet a staged rollout can prevent the remediation itself from interrupting a critical upload service.
Curl maintains separate release information for standard versions and its Rock-solid branches. Organizations that consume a supported long-term branch should check whether the appropriate branch release is 8.14.3, 8.16.2, or 8.20.2 rather than replacing it blindly with the newest standard branch. The governing question is not “what number did the upstream command-line download page show?” It is “which supported package contains the fix for CVE-2026-92392, and how can we prove that package is deployed?”
A practical inventory for this vulnerability
Start with the obvious installations, but do not stop there. Search endpoint and server images for the curl executable, query operating-system package managers, inspect container layers, review software bills of materials, and examine build manifests for libcurl. Package names vary: a host may expose curl, libcurl, a development package, or a vendor-specific runtime bundle. Static linking can remove the library from the host’s ordinary package database, so application release manifests and SBOMs are valuable evidence.
Then add behavior to the inventory. The highest-priority records are processes that do all of the following:
- run a vulnerable curl or libcurl build;
- upload files or request bodies to a remote service;
- permit HTTP/2 negotiation or explicitly enable HTTP/2; and
- handle data or credentials whose loss would matter.
A vulnerable library used only for local metadata parsing should not receive the same immediate treatment as a public-facing automation service that uploads credentials, build artifacts, customer documents, or backups. Risk ranking should account for destination control as well. A fixed allowlist of vendor endpoints is a different exposure from a tool that accepts an arbitrary URL from a user, job parameter, webhook, or remote configuration file.
For statically linked or opaque products, ask the supplier for three concrete answers: whether the product includes curl or libcurl in the affected range, whether HTTP/2 uploads are possible, and which build contains the fix. Keep the answer with the asset record. “The product uses HTTPS” is not a sufficient assessment, and “the product does not expose curl in its user interface” is not an answer about its embedded dependencies.
Container environments deserve an additional check. Updating the host does not update an old image, and rebuilding an application image does not necessarily replace a curl library copied into a final stage. Scan both the image currently running and the image that will be promoted next. If an orchestrator retains old replicas during a rolling deployment, confirm that every active replica has left the affected range before closing the incident or vulnerability ticket.
Temporary mitigations while patches move
The curl advisory lists avoiding HTTP/2 as a fallback when upgrading or patching is not immediately possible. That is a mitigation, not a substitute for remediation. For a command-line workflow, an operator may be able to force HTTP/1.1 for a narrowly defined transfer. For an application, the equivalent setting may be a library option, a proxy policy, a service-mesh rule, or a vendor configuration. The control must be tested: disabling HTTP/2 in one wrapper does not help if the underlying application opens a separate connection through another code path.
A temporary protocol restriction can also have side effects. Some services require HTTP/2, use connection multiplexing for throughput, or apply different authentication and timeout behavior by protocol. Document the exception, identify the owner, and set an expiry date. A mitigation that remains indefinitely because nobody knows whether it is still active becomes another inventory problem.
Where possible, constrain upload destinations during the interim period. Enforce outbound allowlists for automated jobs, reject user-supplied destinations unless the workflow explicitly needs them, and verify redirects rather than silently following a chain to an unexpected host. These measures reduce the chance of a vulnerable client reaching a malicious receiving server, but they cannot replace the patch: a legitimate destination can be compromised, and a broad allowlist may still include attacker-controlled infrastructure.
Do not respond by turning off certificate verification or weakening TLS. The advisory’s exploit conditions include a server that passes the client’s certificate checks, which is a reminder that ordinary transport authentication is not a complete defense against a compromised or maliciously operated endpoint. Removing certificate verification would enlarge the attack surface without addressing the memory-safety bug.
What to examine if a vulnerable client was exposed
A vulnerable version is not proof of compromise, and a crash is not proof of exploitation. Still, an exposed upload client deserves a proportionate review. Identify the destinations contacted during the relevant period, the files or request bodies sent, the exact curl or libcurl build, and whether HTTP/2 was negotiated. Application logs, proxy logs, TLS telemetry, and endpoint process records may answer these questions even when curl itself records only a generic transfer error.
Look for abnormal termination, repeated retries against an unusual endpoint, a change in the child processes launched by an uploader, unexpected files, and outbound connections that began immediately after a failed transfer. These are triage signals, not signatures unique to CVE-2026-92392. A normal upload failure can produce retries and a crash can produce a restart, so interpretation must be tied to the host’s expected behavior.
If the process had access to credentials, tokens, signing keys, or sensitive local files, assess that access separately. The published vulnerability is a client memory-safety problem; it is not described as a direct credential-disclosure bug. Nevertheless, successful code execution in an uploader could expose whatever privileges and data were available to that process. Rotate secrets when the investigation cannot establish that the process remained within its expected boundaries, and preserve relevant logs before routine retention removes them.
For high-value systems, compare the vulnerable build with the fixed build and retain evidence of the update. Capture the package checksum or image digest, the running process version, and the deployment timestamp. If the product vendor supplies a hotfix rather than an upstream release, record the vendor bulletin and the package build identifier. This evidence is more useful than a ticket comment saying “curl patched,” particularly when several copies of the library exist on the same host.
What developers should change
Developers should treat libcurl as part of the application’s security boundary, not as an interchangeable utility hidden below the business logic. Pinning a version in a build file is not enough if the runtime image supplies a different shared library, if a base image is stale, or if a package manager resolves a vulnerable version during a rebuild. Make the dependency visible in the SBOM and make the update path repeatable.
Review upload code for destination control, redirect behavior, retry logic, and protocol selection. A service that uploads only to a fixed endpoint has a different threat model from one that accepts arbitrary URLs. A retry library may perform a second connection using different options from the first. A proxy may negotiate HTTP/2 even when the application did not call that out explicitly. Security review should follow the actual connection path rather than the most convenient configuration file.
Limit the privileges of upload workers. Run them with the smallest filesystem, network, and credential access that the job needs. Use separate identities for reading a local file and publishing it, and avoid giving a generic transfer worker access to cloud-admin credentials, signing keys, or the host’s container socket. Least privilege does not eliminate the vulnerability, but it can turn a code-execution event into a contained service incident instead of a broader host compromise.
Add negative-path tests around interrupted HTTP/2 transfers, server resets, retries, and cleanup. The goal is not to reproduce the exploit in production or to build offensive capability. The goal is to verify that the application handles a failed transfer safely, that the fixed dependency is actually loaded, and that restart and retry behavior do not create a second path around the update.
What operations teams should communicate
The most useful internal notice is precise: CVE-2026-92392 affects curl and libcurl 8.12.0 through 8.22.0; the vulnerable scenario involves an HTTP/2 upload; the fixed upstream release is 8.23.0; and embedded library copies count. Avoid telling every employee to update a browser or to stop using the internet. Most people do not operate the affected upload workflows, and indiscriminate warnings make the next serious alert harder to hear.
Ask service owners to report whether their systems upload data, which destinations they contact, whether HTTP/2 is enabled, and which package or image supplies curl. Give them a temporary mitigation that can be verified and an owner for the permanent update. This turns a broad dependency alert into a set of answerable questions.
The curl project’s disclosure also offers a broader lesson. A mature, heavily scrutinized component can still ship a serious memory-safety flaw. That fact should not produce a panic cycle in which teams replace reliable software with unverified alternatives. It should produce disciplined dependency visibility, faster patch propagation, safer process privileges, and clearer evidence about how network protocols are negotiated.
Bottom line
CVE-2026-92392 is worth prioritizing because it combines a broad dependency footprint with a server-side trigger during client uploads. It is not a universal remote takeover of every curl installation, and the published exploitation conditions are demanding. The absence of a current known-exploitation flag does not make an unpatched upload service a comfortable long-term exception.
Find every curl and libcurl copy, identify which ones upload over HTTP/2, update vulnerable builds to a vendor-supported fixed version, and use HTTP/1.1 or destination restrictions only as temporary controls. Then retain evidence that the running process—not merely the build file or base image—contains the fix. That is the response this vulnerability calls for: specific, dependency-aware, and calm enough to catch the copies nobody remembered were there.
Related articles
CVE-2026-9586 in Switchvox: Patch the PBX, Prove the Fix
Sangoma has fixed a Switchvox flaw that can lead from unauthenticated SQL injection to remote code execution. Here is how to identify exposed systems, update safely, check for prior compromise and communicate the risk without panic.
CVE-2026-75650 in Adobe Commerce and Magento: Patch the Store, Then Investigate It
Adobe says CVE-2026-75650 is being exploited in the wild. The emergency fix closes a critical unauthenticated code-execution path, but merchants must also determine whether attackers reached the store before the hotfix was available.

CVE-2026-76461: Cisco Secure Email Gateway Users Need a Patch-and-Forensics Response
Cisco says an unauthenticated SQL injection flaw in Secure Email Gateway is being actively exploited. The right response is broader than upgrading: identify every appliance, install the fixed AsyncOS release, and inspect mail logs for evidence of compromise.
CVE-2026-9586 в Switchvox: как закрыть уязвимость без паники
Зафиксирована реальная попытка эксплуатации CVE-2026-9586. Разбираем, какие системы Switchvox необходимо проверить, как безопасно установить обновление и почему после исправления может потребоваться расследование.
Comments
Sign in to comment.
No comments yet.