Apple’s Full Disk Access warning makes desktop AI permissions an IT control problem
Apple says macOS will add stronger safeguards around Full Disk Access as AI agents make broad desktop permissions more consequential. The practical response is to inventory, narrow, and review agent access before the new controls arrive.
Apple has announced additional controls for Full Disk Access in macOS, a permission that can let an application reach files, mail, messages, and browsing history across a Mac. The company says the change is necessary because some developers are using the permission in ways that can expose sensitive information without users fully understanding what they have approved. Apple also makes the connection to AI agents explicit: as agents become more capable and autonomous, the risks associated with broad access will increase.
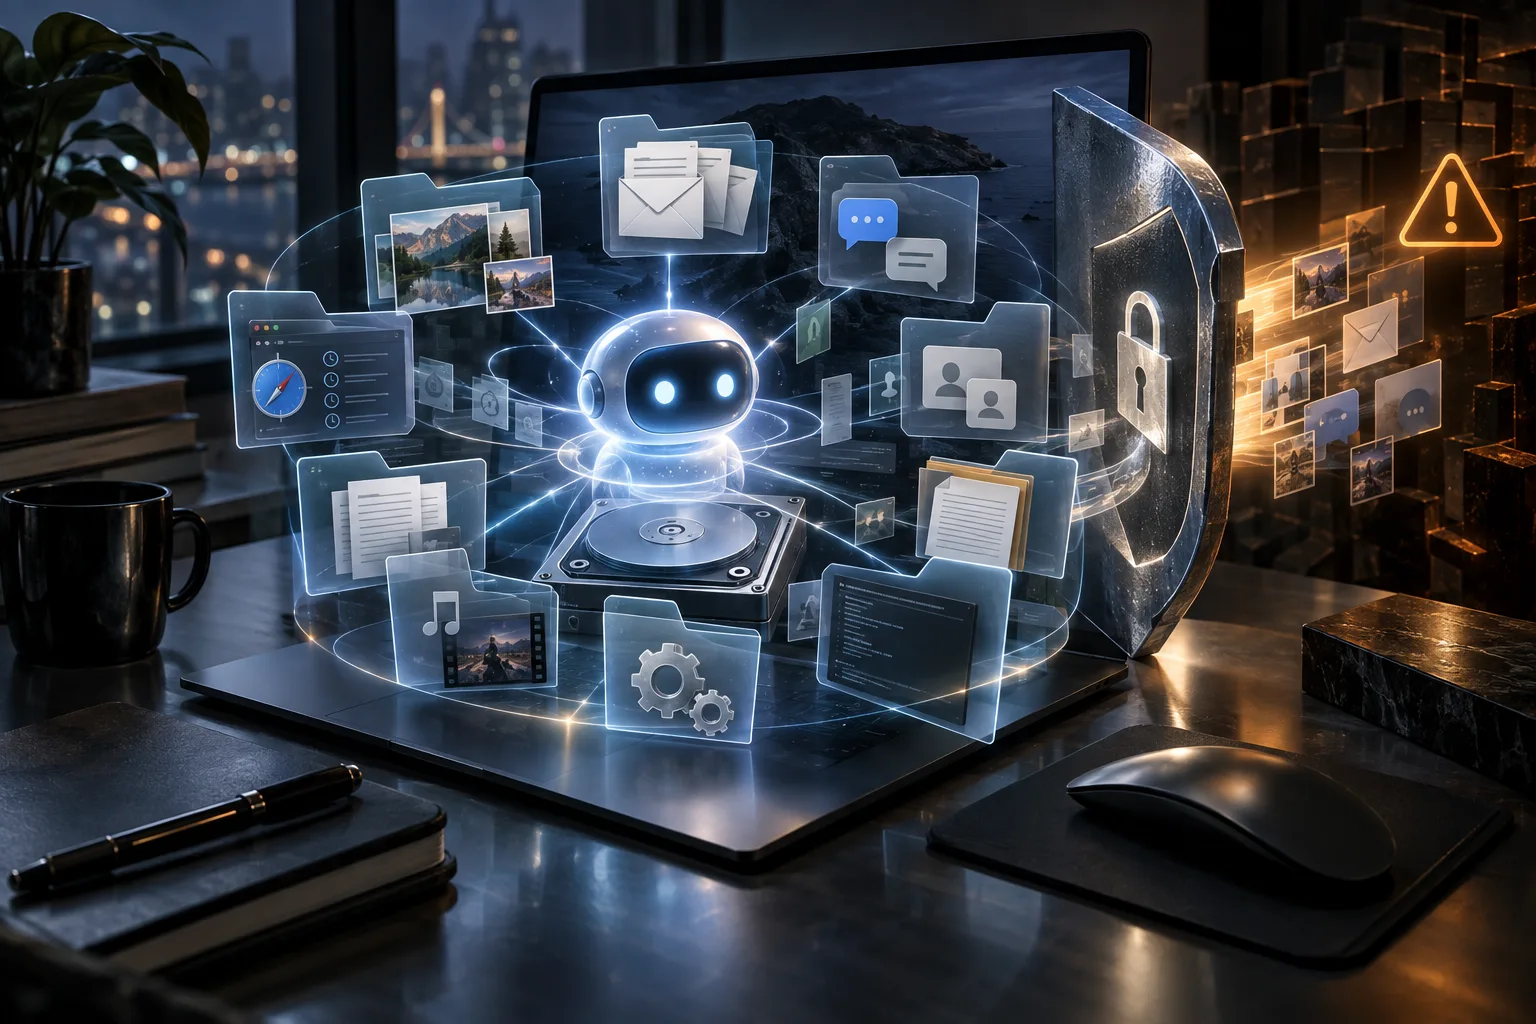
The announcement is short on implementation details. Apple has not named a macOS release, provided an API specification, described a new entitlement, or published a rollout date. That uncertainty matters for developers, administrators, and users. It would be easy to treat the statement as a future privacy refinement that can wait for a software update. The more useful reading is operational: Apple is signaling that a permission designed for exceptional desktop utilities is no longer a comfortable default for software that can interpret instructions, select tools, inspect many data sources, and act without a person approving every individual step.
For IT teams, the immediate task is not to guess which future dialog Apple will ship. It is to understand where broad permissions already exist, decide which workflows genuinely need them, and establish a review process for agents that can operate on a user’s machine.
What Apple actually announced
Apple’s October 2 developer notice describes Full Disk Access as a mechanism that largely bypasses macOS privacy controls so that applications such as backup tools can function properly. A backup product may need to read data in many locations, including places that ordinary applications cannot access through the normal per-folder or per-file consent model. That is the original operational logic for a permission with such a wide scope.
The company now says that some developers are using the capability in ways that could put users at risk. Apple specifically names files, mail, messages, and browsing history as categories that may be exposed. It also warns that, for communication applications, the privacy impact can extend to the people communicating with the user. A message database is not only the account holder’s information; it contains content created by colleagues, customers, family members, and other third parties.
Apple’s promised remedy is additional control before an application receives this level of access. Users who genuinely want to grant it should have to take “very explicit user action,” in Apple’s wording, and should clearly understand the privacy consequences. The announcement frames the change as a protection for informed consent, not as a blanket ban on Full Disk Access. Backup software and other legitimate workflows may continue to need exceptional access.
That is the complete public commitment so far. Apple has not said whether the change will affect existing grants, new installations, background helpers, managed Macs, notarization, the Mac App Store, or developer review. It has not said whether a user will be able to grant access temporarily, limit it to a selected data class, approve it per task, or delegate it through a management profile. Any article claiming those details are already decided would be going beyond the announcement.
Why AI agents change the meaning of the permission
A conventional application usually has a relatively stable purpose. A backup tool reads data, packages it, and sends it to a destination. A search indexer scans files. A communication tool handles messages. These applications can still be compromised or misused, but their expected actions are comparatively bounded.
An agent is different because its behavior is partly determined at runtime. It may receive a natural-language request, inspect the local environment, choose among tools, read files for context, call a service, edit documents, send a message, or continue through several steps. The agent’s usefulness comes from crossing boundaries that ordinary applications often keep separate. The same flexibility makes an overly broad permission more consequential.
Full Disk Access does not make an agent intelligent, trustworthy, or safe. It simply removes a major access barrier. Once that barrier is gone, the agent’s model, tools, plug-ins, background processes, network connections, prompt sources, and credential handling all become part of the effective trust boundary. A local model with blanket access still has blanket access. Running an agent on-device may change where inference occurs, but it does not narrow what the application can read or modify.
The risk is not limited to a deliberately malicious developer. An agent can be given a legitimate task and still encounter untrusted instructions in a document, web page, repository, message, or issue tracker. If the agent can read that material and also has powerful tools, content that was supposed to be data can influence what the agent does next. Broad operating-system permissions amplify the result. A suspicious instruction is more serious when the process that reads it can also access private mail, modify files, or send data through an authenticated account.
This is why Apple’s notice is more significant than a routine privacy-settings adjustment. The company is recognizing that permission design has to account for software that is not merely displaying information or responding to a button press. Desktop agents compress reading, decision-making, and action into one workflow. A permission that was tolerable for a narrowly defined utility can become excessive when attached to a general-purpose operator.
The announcement follows a wider platform shift
Apple has spent 2026 making agentic capabilities more visible in its own developer tools and operating systems. Its WWDC materials describe agentic coding in Xcode, including agents that can plan work, use tools, validate results, and operate for longer periods. Apple’s platform releases also describe broader system actions and personal-context features for Siri AI. Those products may use different controls and system architecture from third-party desktop agents, but they raise the same design question: what should software be able to see and do, and how clearly is that authority presented to the person using it?
The difference between first-party and third-party software should not be reduced to a claim that one is automatically safe. Apple’s own platform privileges, system services, and privacy architecture are managed under a different trust model from an independently distributed Mac application. For enterprise administrators, the relevant question is not whether an agent carries an Apple, vendor, or open-source label. It is whether the organization can identify its permissions, constrain its data, review changes, revoke access, and investigate actions afterward.
The announcement also lands alongside a separate industry effort to make agent authority more portable and reviewable. Docker’s Sandbox Kit specification proposes packaging an agent, its tools, and a typed declaration of requested hosts, credentials, and volumes in an OCI image. That initiative does not change macOS permissions and is not an Apple policy. It is useful context because it reflects the same underlying problem from the infrastructure side: teams need to review what an agent is allowed to reach as an explicit artifact, rather than infer authority from scattered setup instructions.
These efforts are not interchangeable. A container or sandbox can reduce the blast radius of an agent, while Full Disk Access is an operating-system permission on a user’s Mac. A portable declaration is only valuable if a runtime enforces it. Still, the direction is consistent. Agent access is moving from informal configuration toward a security control that should be declared, compared, approved, and logged.
Who is affected first
Mac users running desktop agents
The most immediate group is people who have installed agents that can operate outside their application window. This includes coding assistants, research tools, productivity agents, automation utilities, and applications that can control other Mac software. The label “AI” is not enough to determine risk. A tool that only answers questions inside a sandbox may need little access. A tool that searches the whole home directory, reads messages, edits repositories, launches commands, and uses browser sessions deserves a much more careful review.
Users should pay attention to the difference between a narrowly scoped file or folder permission and Full Disk Access. Granting access to a project directory is materially different from granting access to mail stores, browser data, application support directories, and other protected locations. A request for broad access may be legitimate, but convenience is not a sufficient reason to approve it.
Developers of Mac applications
Developers should expect more scrutiny around requests for exceptional access. Apple’s statement does not announce a new review rule, but it clearly says that the current pattern creates user risk. Applications that currently request Full Disk Access during onboarding should be prepared to explain why, delay the request until the feature needs it, and provide a useful experience when the user declines.
The technical documentation already advises developers to handle cases where a user does not grant Full Disk Access. That guidance becomes more important when the application includes an agent. A robust design should not make the broadest permission the hidden prerequisite for basic functions. If an agent needs to work on a selected project, a folder-scoped workflow is easier to explain and safer to operate than a request to inspect the entire Mac.
Enterprise and managed-device teams
Organizations may be affected before the new control ships. Help-desk teams will receive questions about why an agent cannot read a file, why an automation stopped working, or whether a permission should be approved for an executive or developer. Security teams may discover that a software inventory records the application but not its effective privacy grants. Mac administrators will need to connect endpoint management data with application inventory, identity controls, and data-loss monitoring.
The key issue is not simply whether Full Disk Access is enabled. It is the relationship between the permission and the agent’s other authorities. An agent with full-disk read access, a browser session, a source-control token, and permission to send mail has a different risk profile from an agent with the same disk permission but no network or account access. Treating each permission in isolation can hide the combined capability.
What IT teams can do now
The following actions do not depend on Apple publishing the final implementation. They are useful for current macOS fleets and for any organization evaluating desktop agents.
Build an inventory of effective access
Start with the applications that have Full Disk Access on managed Macs. Record the application identity, publisher, version, installation source, business owner, user population, and reason for access. Include background helpers and companion processes where the management platform exposes them. An inventory that lists only the visible application name may miss the component that actually performs automation.
Add the permissions that create compound risk: access to Mail or Messages, browser automation, accessibility control, shell or scripting tools, login items, background execution, cloud drives, source-control credentials, and API keys. The goal is not to create a frightening list of every permission. It is to identify combinations that let software read broadly and then act externally.
Classify agents by task boundary
Create a simple classification based on what the agent is expected to touch. A project-scoped coding assistant, a document summarizer restricted to a shared folder, and a general desktop operator should not receive the same default profile. Define the permitted data area, allowed applications, network destinations, credential types, and whether human approval is required before an external action.
A useful policy sentence is specific: “This agent may read and modify files under the approved repository, run the approved test commands, and open a pull request, but it may not read personal messages, access browser cookies, send email, or change production infrastructure.” The exact boundary will vary by role. The important part is that the boundary describes actions and data, not just a product name.
Remove access that is not needed
Review existing grants instead of waiting for a migration project. If a user enabled Full Disk Access to test a feature and no longer needs it, revoke it. If an application can work with a selected folder, move the workflow toward that narrower model. If a vendor’s instructions say to enable the permission but do not explain the feature that requires it, ask for clarification before approving it across a fleet.
Do not assume that a permission becomes safe because the agent is local, open source, or popular. Those traits may matter to the threat model, but they do not replace access control. A process that can read the whole disk can still expose sensitive material through logs, tool calls, generated files, telemetry, or an accidental action.
Establish approval and review for agent changes
Agent capabilities change quickly. A software update may add a browser connector, a new plug-in system, a shell tool, or a background helper. Treat a request for additional data or network access as a security-relevant change, even if the vendor presents it as a feature update. Require the application owner to document the new capability and the reason it is needed.
For higher-risk workflows, compare the declared access between versions and keep a record of approvals. The review should include what data the agent can read, what actions it can take, what credentials it can use, and how access is revoked. This is especially important for agents that can install dependencies, edit automation files, open pull requests, or communicate with customers.
Use separate accounts and data where possible
An agent should not automatically inherit the full authority of a person’s everyday account. Use dedicated identities, narrowly scoped tokens, separate browser profiles, and test repositories for tasks that do not require personal data. Keep production credentials outside the agent’s default environment. Require a deliberate handoff for actions that create financial, legal, customer, or production consequences.
This approach reduces the value of an accidental instruction in a document or message. It also improves investigation because the organization can distinguish an agent action from a person’s normal activity. Separation cannot eliminate every risk, but it prevents one broad desktop grant from becoming an all-purpose key.
What developers should change in product design
Apple’s notice is also a prompt to revisit the user experience of permissions. Asking for Full Disk Access on first launch, before the user has seen the value of the application, creates a poor basis for informed consent. It encourages users to click through a high-impact request as part of installation.
A better sequence is to start with the narrowest capability, explain the specific task that needs more access, show what categories of data will become reachable, and let the user approve that step at the moment of need. If the product cannot operate without broad access, say so plainly. Do not describe a system-wide grant as a routine “setup” step.
Agent interfaces need an additional layer of explanation. Users should be able to see which tools the agent may call, which folders are in scope, what network destinations are allowed, and which actions require confirmation. A model’s conversational confidence is not a permission boundary. The interface should make authority visible even when the agent’s response sounds harmless.
Applications should also preserve useful audit information. A user or administrator should be able to determine which files were accessed, which tool was invoked, which external service received data, and when an action occurred. Logging must be designed with privacy in mind, but an agent that can operate broadly without producing an understandable record is difficult to govern.
What remains unknown
Apple’s statement leaves several practical questions unanswered. The company has not said when the new controls will appear, whether they will arrive in a macOS update or a later major release, or how existing Full Disk Access grants will be handled. It has not described the user interface, management controls, developer APIs, or enforcement mechanism.
It is also unclear whether Apple will introduce finer-grained alternatives for common agent workflows. A selected-folder grant, per-application automation permission, task-scoped approval, or time-limited access could reduce pressure to request Full Disk Access. Those are plausible design directions, not announced features. Organizations should not build a compliance plan around any one of them until Apple documents the behavior.
The timing of enforcement is equally important. A stronger user prompt may improve consent without reducing the agent’s technical authority after approval. Conversely, a narrower API could require meaningful application redesign. Apple’s language supports the conclusion that the consent path will change; it does not yet support a conclusion about the final security model.
The practical conclusion for today
Apple has identified a mismatch between an old permission model and a new class of software. Full Disk Access was created for applications with legitimate reasons to inspect a Mac broadly, particularly backup workflows. AI agents make the same permission more powerful because they can interpret changing instructions and connect access to tools and actions.
The near-term response is governance, not speculation. Inventory broad permissions. Remove grants that no longer have a clear purpose. Separate project work from personal data. Use dedicated credentials. Define what each agent may read and do. Review capability changes as security changes. Require confirmation before consequential external actions.
When Apple publishes the technical details, organizations that have already mapped their agent access will be able to adapt quickly. Those that have treated permissions as a one-time installation checkbox will first have to discover what their software can already see.
Related articles
AWS Lambda MicroVMs make AI-agent sandboxes easier to deploy—and harder to govern by accident
AWS’s new Lambda MicroVM reference architecture gives teams fast, isolated execution environments for AI-agent tasks. The important change is operational: identity, egress, persistence, observability and cleanup now need to be designed as one system.
Google’s policy week shows browsers and app stores are IT infrastructure
Manifest V2 removal, uBlock Origin’s Chrome Web Store exit, AnkiDroid’s donation-link fight and Aurora Store friction all point to one risk: client-platform control.
Home Assistant keeps failing? Start with the storage, not the dashboard
Raspberry Pi and Orange Pi smart-home setups often fail at the least glamorous layer: microSD cards, USB sticks, power supplies and missing backups. Here is how to move toward SSD, Data Disk or a mini PC without losing the house.
When a phone camera turns an eclipse into the Moon: the Xiaomi 17 Ultra lesson
A reported Xiaomi 17 Ultra eclipse photo shows why buyers need to understand AI camera modes, RAW capture and the difference between enhancement and evidence.
Comments
Sign in to comment.
No comments yet.